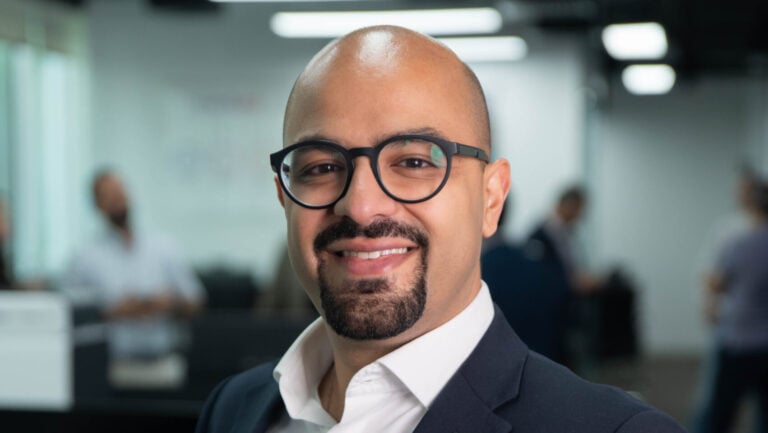
Rebecca Spayne of Security Buyer talks exclusively with Hillary Baron, Senior Technical Director, CSA and Tyler Young, CISO for BigID
Could you provide us a background into the history and heritage of the CSA?
The idea for Cloud Security Alliance was born in 2008 at the ISSA CISO Forum, and by the 2009 RSA Conference, the group counted dozens of volunteers ready to research, author, edit and review CSA’s first whitepaper. The following year, CSA released the Cloud Controls Matrix (CCM), the industry’s de facto cybersecurity control framework for cloud computing, along with the first and only user credential for cloud security, the Certificate of Cloud Security Knowledge (CCSK). In 2013, CSA launched the CSA Security, Trust, Assurance and Risk (STAR) program, a powerful program for security assurance in the cloud. In the years that have followed, CSA has opened offices in the UK, APAC, and Europe, and remains an organisation dedicated to defining standards, certifications and best practices to help ensure a secure cloud computing environment.
The CSA recently released, in coordination with BigID, the results of a survey on cloud data security. Why was this survey conducted initially?
Security strategies focusing on data security have been gaining attention over the past year. CSA and BigID decided we needed to dig into the topic further to understand what organisations are currently doing for cloud data security, what aspect they are prioritising, and the concerns and challenges these organisations are facing with cloud data security.
What were some of the key findings of the survey?
One of the biggest takeaways from this survey shows organisations consider cloud data security a top 3 priority when protecting data, and that cloud data security posture management (DSPM) is critical to addressing gaps.
- Only 4% believe all of their cloud data is sufficiently secured and over a quarter of organisations aren’t tracking regulated data.
- Organisations are struggling with securing and tracking sensitive data in the cloud, especially in SaaS platforms.
Another key takeaway is that most security professionals believe their enterprise will experience a data breach in the next year. Only 17% say that a breach is very unlikely.
- Third-party vendors have too much access to sensitive data. They’re being granted almost the same level of access as employees are, which can result in breaches.
- It’s all going to boil down to the notion that data breaches aren’t an if, but a when—whether it’s malicious or accidental, whether the entry point is a phishing attempt, a back door, or a misconfiguration. Data is the new perimeter these days, so cybersecurity across all of these organisations needs to take a data-up approach.
The pandemic forced digitalisation on many businesses, however, it also forced innovation and subsequent popularity of emerging technologies. Do you think IoT, AI, Blockchain etc will play a bigger role in the security industry?
Short answer, yes, especially with the skills gap and the recent pandemic in the security industry, organisations are having to rely on and be more innovative with how they’re using technology. These types of technologies are also being integrated into products that we already use in technology, which means there will be a direct impact on security. To use IoT as an example, almost anything can be an IoT device including the breakroom coffee maker and even lightbulbs, which means the security of that device has a direct impact on your enterprise’s overall security.
Attackers are leveraging AI in terms of identifying targets and changing their TTPs—this is nearly impossible for a human to keep up with, and thus we will be forced to leverage machine learning and AI for combating threats.
What is a zero trust strategy, and what training do you provide in this area?
A Zero Trust strategy follows the model of least privilege, which says that no part of a computer and networking system—including the people operating it—can be implicitly trusted. This means access is withheld until the user, device, or individual packet has been inspected and authenticated. When access is granted, the least amount of necessary access is provided and there is continuous monitoring for suspicious user activity. Because it incorporates several: including identity, devices, networks, applications, and a Zero-Trust strategy isn’t achieved through a single product.
In 2022, CSA, with Crowdstrike, Okta, and Scaler, established the Zero Trust Advancement Center (ZTAC) to create Zero Trust research, training, professional credentialing, and an online center for curated resources. The ZTAC includes the Zero Trust Resource Hub showcasing the most important, curated Zero Trust publications in the industry and the online Zero Trust Training program, which gives users the knowledge and skills they need to understand and implement a Zero Trust strategy. Eight areas of Zero Trust knowledge will be covered and are being rolled out, beginning with Introduction to Zero Trust Architecture, which covers such foundational topics as Zero Trust’s relevance, definitions, components, requirements, tenets, pillars, goals, objectives, and benefits. Introduction to Software Defined Perimeter and SDP Key Features and Technologies and SDP Architectures and Components will follow later this year.
What is your STAR Program?
CSA’s STAR Registry is a publicly accessible registry of more than 1,800 providers that documents the security and privacy controls provided by popular cloud computing offerings. STAR encompasses the key principles of transparency, rigorous auditing, and harmonisation of standards outlined in the CCM. Publishing to the registry allows organisations to show current and potential customers their security and compliance posture, including the regulations, standards, and frameworks they adhere to. It ultimately reduces complexity and helps alleviate the need to fill out multiple customer questionnaires.
To read the full exclusive see our latest issue here.
Never miss a story… Follow us on:
 Security Buyer
 @SecurityBuyer
 @Secbuyer
Media Contact
Rebecca Morpeth Spayne,
Editor, Security Portfolio
Tel: +44 (0) 1622 823 922
Email: [email protected]