

Right to be Forgotten and EU GDPR: A Corporate Dilemma
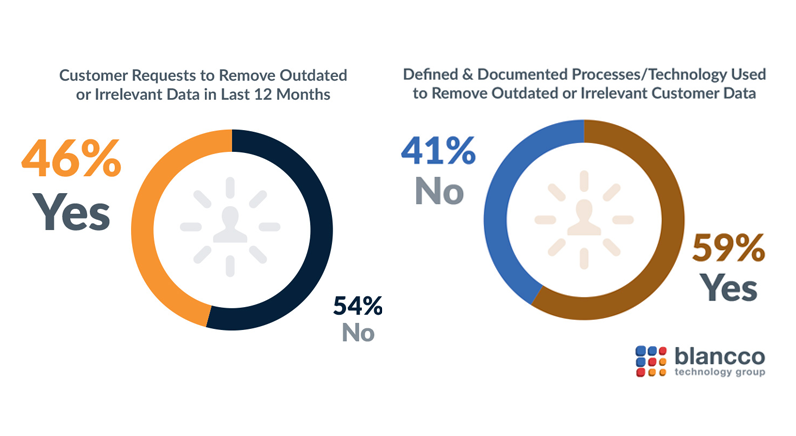
IT governance & technology deficiencies impede organisations from complying with “Right to be Forgotten” & EU GDPR by 2018 – although 46 percent of global organisations received customer requests to remove data in last 12 months, 41 percent lack defined processes, documentation and technology, according to Blancco Technology Group study.
To kick off the formal ratification of the EU General Data Protection Regulation by the European Council in early 2016, Blancco Technology Group has released its new data privacy study, EU GDPR: A Corporate Dilemma. Based on a survey of over 500 global IT professionals across more than 20 types of businesses, the study indicates that organisations lack defined processes, documentation and technology to adequately address the “right to be forgotten” and require major overhauls of their data collection and removal programs to ensure EU GDPR compliance. Although 46 percent of global IT professionals received customer requests to remove data in the last 12 months, 41 percent said they do not have defined processes, documentation and technology/tools for data removal.
“Because the EU GDPR negotiations stretched on for the last four years, many organisations held out hope that an agreement would be postponed, or if things went the way they hoped, the negotiating parties would never come to agreement,” said Pat Clawson, CEO of Blancco Technology Group.
“But now that the EU GDPR is a reality and the new privacy rules will be ratified by the European Council in early 2016, many organisations have a considerable amount of work ahead of them to align their IT governance and data protection programs with both regulatory and customer demands.”
Key corporate security trends that surfaced from the study include:
- While awareness of GDPR is high (48 percent) among global IT professionals, their level of preparation is much lower. 40 percent admit to being less than fully prepared – with 16 percent still needing to find the right data removal software, 9 percent uncertain of how and where to start, and finally, 15 percent not even knowing if they are prepared.
- Lack of documentation, processes and tools increases the likelihood of GDPR violations. 60 percent of the surveyed IT professionals stated that it would take their organisation up to 12 months to implement the necessary IT processes and tools to pass a “right to be forgotten” audit, while 25 percent do not know how long it would take.
- Data erasure software (48 percent) tops the list of the most valuable type of technology to ensure GDPR compliance, followed by encryption key removal tools (26 percent) and malware removal tools (10 percent).
- IT professionals inside and outside of Europe (65 percent) are keen to implement data protection laws similar to the framework of EU GDPR.
Clawson concluded:
“If organisations want to be ready for GDPR compliance by 2018, they will need to assess their current weaknesses. Once they have done so, they will need to develop end-to-end data lifecycle management processes, create transparent processes and customer communications regarding their data removal methods/tools, and finally, improve their security posturing as a whole to include detection and response and the gathering and sharing of threat intelligence.”
Due to the stringent requirements and penalties imposed by the new law, companies are advised to follow a 12-step action plan to fully prepare for compliance by 2018.
Survey Methodology:
We surveyed 511 corporate IT professionals in the United States, Canada, Mexico, United Kingdom, Germany, Singapore, Malaysia and Australia to understand their level of awareness, preparation and capacity to comply with the ‘right to be forgotten’ and the General Data Protection Regulation. The survey was fielded during Fall 2015 and targeted IT professionals across a variety of businesses (up to 10,000 employees) and represents 20 different business categories.
Blancco Technology Group is a leading, global provider of mobile device diagnostics and secure data erasure solutions. We help our clients’ customers test, diagnose, repair and repurpose IT devices with the most proven and certified software. Our clientele consists of equipment manufacturers, mobile network operators, retailers, financial institutions, healthcare providers and government organisations worldwide. The company is headquartered in Alpharetta, GA, United States, with a distributed workforce and customer base across the globe.
[su_button url=”http://www2.blancco.com/EU-GDPR-Corporate-Dilemma-Research-Study” target=”blank” style=”flat” background=”#df2027″ color=”#ffffff” size=”10″ radius=”0″ icon=”icon: arrow-circle-right”]Click here to read the full Blancco Technology Group study[/su_button]












