
Bethany Kellock examines how banking security systems operate in real-world conditions, where access control architecture, and asset traceability must withstand scrutiny, not theory
Banking security is often discussed in terms of layers, but in practice it behaves more like a chain. Each component is dependent on the integrity of the one before it, and failure is rarely isolated.
The industry has spent the past decade focusing on digital transformation, but physical and electronic security systems have not become less relevant as a result. They have become more exposed. The shift towards distributed banking, smaller branches, automated services, and centralised operations has reduced physical presence while increasing the value of what remains.
Cash handling sites are fewer, but more concentrated. Data centres are more critical. Remote access has increased, but physical intervention points have not disappeared. What has changed is the tolerance for inconsistency. Systems that were once independent now sit under regulatory and operational scrutiny that expects continuity, auditability, and verifiable control.
The question is no longer whether a system works. It is whether it works under pressure, across sites, and without relying on assumptions.
Vaults are no longer static systems
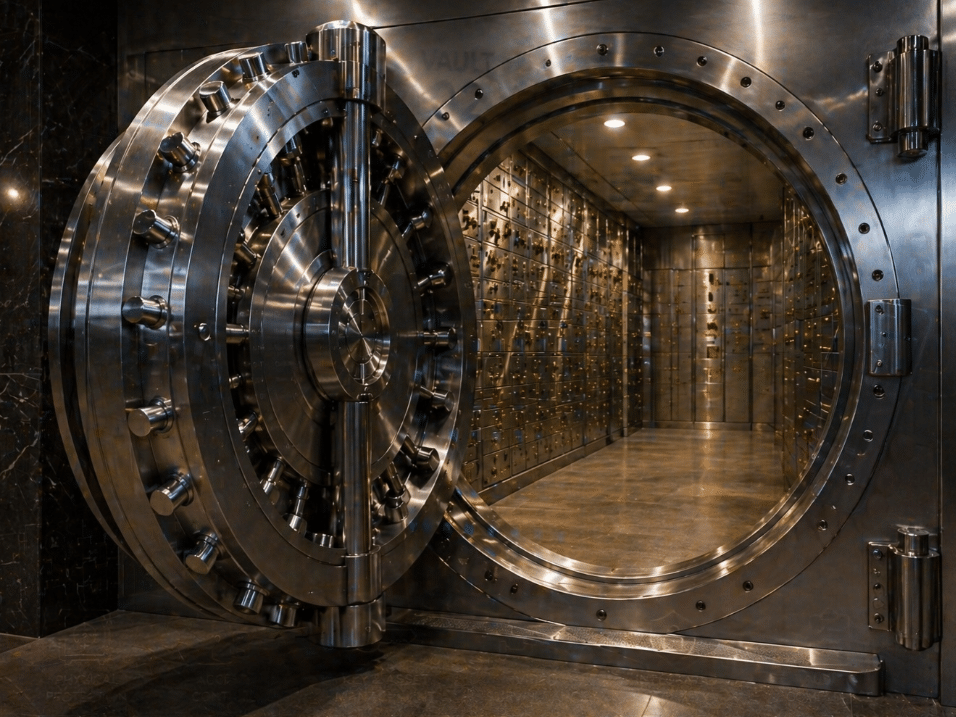
Gunnebo Safe Storage sits in a category that is often misunderstood because it is too easily reduced to hardware. A vault is not simply a reinforced structure. In a banking environment, it is a controlled system with defined operational logic.
Time delays, dual control, and access scheduling are not optional features. They are mechanisms designed to remove single points of failure, particularly human ones. The technology embedded within modern safe storage reflects this. Electronic locking systems now operate with programmable access windows, audit trails, and integration into wider security platforms.
What is often overlooked is how these systems behave operationally. A time delay is not just a deterrent, it is a procedural enforcement tool. It ensures that access cannot be granted impulsively or under duress without triggering a measurable response window.
In high-value environments, dual control mechanisms are still standard, requiring two authorised individuals to complete an action. This is not legacy thinking. It is a recognition that identity systems, however advanced, still operate within human workflows.
The technical challenge is not in building stronger vaults. It is in ensuring that access logic remains consistent across sites and cannot be bypassed through process gaps. This is where integration becomes less relevant than enforcement. A system that integrates but does not enforce is effectively decorative.
Access control is a data problem, not a door problem
Access control in banking is frequently described in physical terms, doors, readers, credentials, but the underlying issue is data integrity.
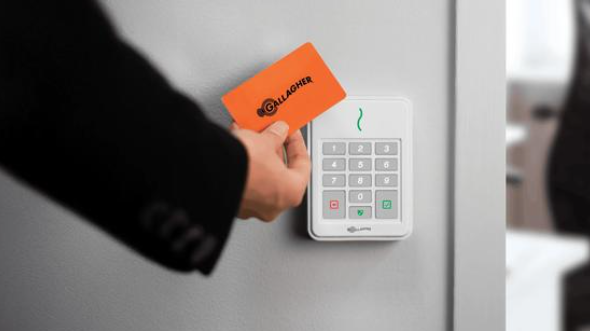
Gallagher Security and AMAG both operate at the level where access decisions are made through policy engines rather than simple credential checks. This distinction matters. In modern banking environments, access is conditional. It depends on time, role, location, and sometimes behaviour.
A credential alone is insufficient. The system must evaluate whether access is appropriate at that moment.
This introduces a technical challenge around synchronisation. Permissions are often managed centrally, but enforcement happens locally. If there is a delay in updating access rights, or a failure in communication between systems, the result is inconsistency. In banking, inconsistency is risk.
TDSi by Hirsch and Keri Systems operate within environments where scalability and reliability are prioritised over complexity. Their systems are often deployed in distributed branch networks, where connectivity may not always be guaranteed. This changes the design requirement.
In these scenarios, access control systems must be capable of operating автономously while maintaining alignment with central policy. That requires local decision-making capability, secure data caching, and controlled synchronisation processes.
This is not a theoretical issue. In real deployments, network interruptions, latency, and configuration drift all occur. Systems that cannot handle these conditions degrade quickly, not in functionality, but in trust.