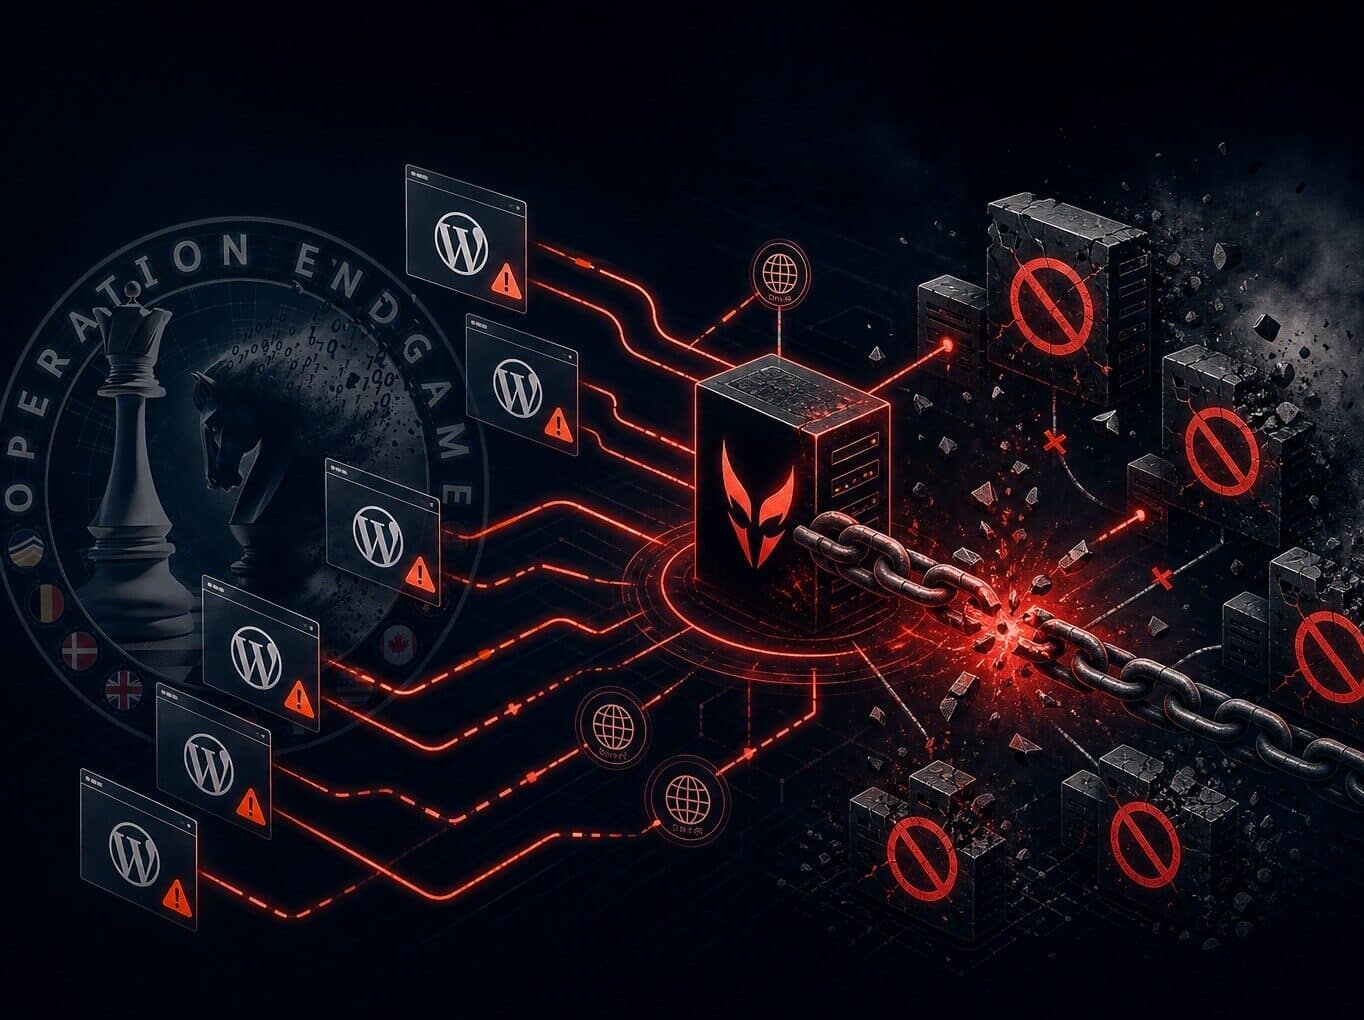

Infoblox has welcomed the latest phase of Operation Endgame, the multinational law enforcement effort targeting infrastructure associated with the SocGholish malware operation, also known as FakeUpdates. The coordinated action resulted in the remediation of nearly 15,000 compromised websites and the disruption of key criminal infrastructure used to distribute malware and facilitate cybercrime.
The operation, led by international law enforcement agencies and coordinated through Operation Endgame, targeted infrastructure linked to the SocGholish ecosystem, a long-running malware distribution network frequently used as an initial access vector for ransomware groups and other cybercriminal organizations. Infoblox is one of the industry partners involved in the action. Authorities announced the takedown of more than 100 servers and domains supporting the operation, representing one of the most significant disruptions of the threat actor ecosystem to date.
Infoblox Threat Intelligence
According to Infoblox Threat Intelligence researchers, the action delivers a substantial blow to a malware operation that has posed a persistent threat to enterprises, government agencies, healthcare providers, educational institutions, and critical infrastructure operators worldwide.
Infoblox researchers assess that Operation Endgame demonstrates the effectiveness of coordinated action between international law enforcement agencies and the cybersecurity community in disrupting sophisticated cybercriminal operations. SocGholish has remained one of the most effective malware delivery mechanisms on the internet because it exploits user trust through compromised legitimate websites and convincing browser update lures designed to deliver malicious payloads.
Infoblox has closely tracked SocGholish activity and its supporting infrastructure for several years. The company’s latest analysis found that nearly 55% of Infoblox cloud security customers encountered SocGholish-related activity during 2026, highlighting the extensive reach and continued effectiveness of the threat despite ongoing awareness efforts and security investments.
SocGholish
SocGholish typically infects legitimate websites and injects malicious JavaScript that presents visitors with fraudulent browser update notifications. When users download the purported update, malware is installed on their systems, providing attackers with an initial foothold that can be leveraged for further compromise. The malware has been linked to multiple cybercriminal groups and has served as a gateway for ransomware deployment, credential theft, financial fraud, and other malicious activities.
The latest phase of Operation Endgame highlights the growing importance of international collaboration in combating cybercrime. By disrupting infrastructure used to distribute malware at scale, law enforcement agencies have increased operational costs for threat actors and interrupted a critical component of the cybercriminal ecosystem.
However, Infoblox cautions that while the operation represents a significant disruption, threat actors frequently adapt their infrastructure, modify tactics, and seek alternative distribution mechanisms. Previous law enforcement actions against major cybercrime operations have demonstrated that adversaries often attempt to rebuild their infrastructure or shift to new delivery methods following successful takedowns.
For this reason, organizations should view the operation as an opportunity to strengthen their security posture rather than assume the threat has been permanently eliminated. Continuous monitoring, threat intelligence-driven defenses, and proactive security controls remain essential for mitigating the risk of malware-based intrusions.
Infoblox researchers note that the broader challenge extends beyond any single malware family. Modern cybercrime operations rely on interconnected ecosystems that include compromised websites, traffic distribution systems, malicious advertising networks, malware delivery platforms, and monetization mechanisms. While disrupting one component can have significant downstream effects, cybercriminals often seek to replace lost infrastructure and restore operations over time.
As attackers increasingly exploit trusted web properties and legitimate-looking content to deliver malware, organizations require greater visibility into malicious activity before it reaches endpoints. Infoblox recommends strengthening DNS-layer security, integrating actionable threat intelligence into security operations, deploying advanced endpoint protections, and maintaining user awareness programs designed to reduce the success of social engineering attacks.
The company also emphasized the critical role that public-private collaboration continues to play in disrupting cybercriminal infrastructure. Successful operations such as Operation Endgame are often the result of years of intelligence gathering, technical analysis, infrastructure mapping, and information sharing among law enforcement agencies, security researchers, and industry partners across multiple jurisdictions.
“SocGholish is not a niche threat. Their activities reach deep into public sector and commercial environments, paving the way for other cybercriminals to gain access to networks”, says Dr. Renée Burton, Vice President of Infoblox Threat Intel. “We are proud to be a partner in Operation Endgame; TA569 and their affiliates have likely had a very bad week. That said we will continue tracking how this ecosystem evolves, whether old partnerships re-emerge, and what new infrastructure or delivery chains may take shape in response.”