
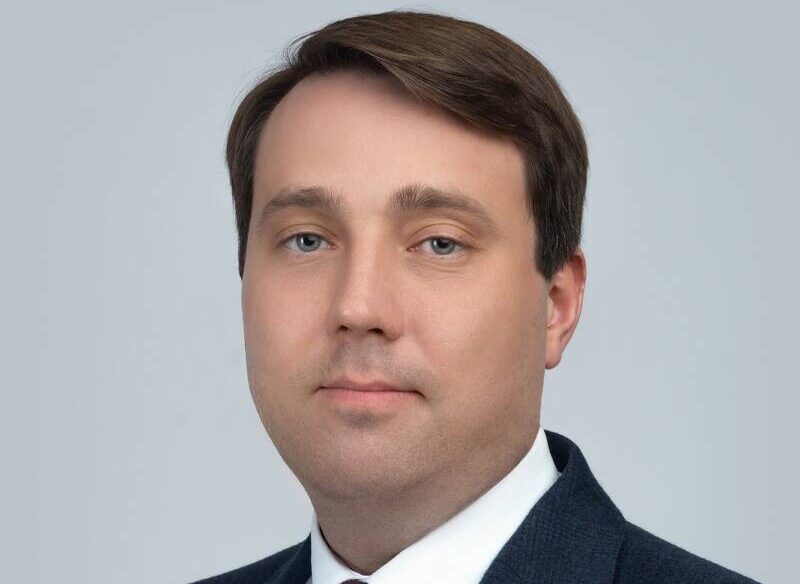

Dr. Ilia Kolochenko, Chief Architect, ImmuniWeb and cybersecurity influencer, talks about the proposed mandatory reporting of ransomware attacks and licensing regime
Dr. Ilia Kolochenko is a Swiss cybersecurity expert and a lawyer admitted to practice in Washington, DC. Having over 15 years in cybersecurity and cybercrime investigation, currently he is a Chief Architect & CEO at ImmuniWeb, a global application security company serving over 1,000 enterprise clients from more than 50 countries.
Additionally, Dr. Kolochenko is an Adjunct Professor of Cybersecurity Practice & Cyber Law at Capitol Technology University (Maryland, US). Being a Member of Europol Data Protection Experts Network (EDEN), INTERPOL Digital Forensics Expert Group (DFEG), SANS CISO Network and GIAC Advisory Board, Dr. Kolochenko has authored over 50 articles on cybersecurity and cybercrime investigation.
What are the primary objectives of the UK’s proposed mandatory reporting of ransomware attacks and licensing regime for all payments?
There are several underlying concepts and interrelated objectives. First, the UK government wishes to understand the true scale of now-obscure ransomware attacks and payments. Many businesses never report ransom payments, making it difficult to better prioritise governmental activities and allocate scarce resources to neutralise the most dangerous cyber threats. Second, the UK probably wishes to ban payments to any sanctioned cyber-threat actors thereby disincentivising their attacks against UK companies and organisations. Finally, by imposing a flat ban on ransom payment for critical national infrastructure (CNI) providers, the UK government aims to reduce ransomware attacks targeting CNI providers as cyber gangs will likely never get paid.
How does the proposed UK legislation compare to the existing Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) in the United States?
While both are not in force yet, the UK’s legislation is in the very nascent phase of development and will likely be significantly shaped and adjusted after public consultations and the long way towards becoming a law. On its side, rules under CIRCIA will probably be finalised and enter into force next year or by 2026. Additionally, CIRCIA covers only CNI providers, while the proposed UK legislation reportedly covers all private entities but with more lenient requirements and restrictions compared to the UK public sector and CNI providers specifically.
What challenges might the National Cyber Security Centre (NCSC) face in handling the increased volume of reports resulting from this new legislation?
The key challenge is the eventual social and economic utility of the newly proposed regulatory regime: it is largely uncertain that the financial and operational burden of mandatory reporting and licensing will bring comparable benefits. For instance, the British private sector will unlikely get much value from the new legislation, whilst the already overloaded and understaffed NCSC will probably waste a lot of time on bureaucratic formalities and investigations of penny payments. Finally, some breached organisations – including CNI providers – may eventually have no other choice but to pay in order to restore their operations, eventually concealing the incidents and exacerbating the consequences.
Could the requirement for licensing extortion payments lead to delays or complications for businesses trying to recover from ransomware attacks?
This is exactly what will likely happen if the proposed law will go overbroad and be inflexible, imposing strict and one-size-fits-all disclosure and licensing requirements. Moreover, some businesses may try to find creative ways to pay the attackers, for example, by making a payment from their parent or sister companies in foreign jurisdictions to evade mandatory licensing. British SMEs and other companies sensitive to cashflow problems will probably suffer the most: while the license is being approved, they may already run out of business, leaving people without jobs and clients without goods or services.
What measures can be put in place to prevent cybercriminals from submitting fake reports to mislead or confuse investigations under the new UK legislation?
AI can be pretty helpful here to recognise fakes, fraud and duplicates, however, the technology has to be thoroughly tested and be uninterruptedly supervised by human experts. Reliable training data for this specific purpose does not exist yet, and while one can use synthetic or similar data for AI training, it will probably take several years before the process can be reliably automated. Obviously, traditional security controls will work as well, for instance, by fencing the reporting system from non-UK IP addresses or users that cannot provide some basic identifiers that are normally known only to legitimate business owners.
See our latest issue here.
Never miss a story… Follow us on:
Security Buyer
@SecurityBuyer
@Secbuyer
Media Contact
Rebecca Morpeth Spayne,
Editor, Security Portfolio
Tel: +44 (0) 1622 823 922
Email: [email protected]












