
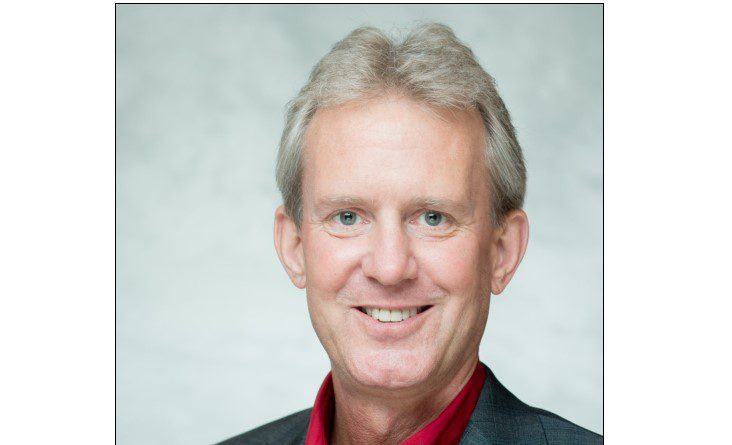

Breaking the myths of zero trust model and understanding how it can protect your organisation – By Dave Russell, Vice President of Enterprise Strategy, Veeam Software
One of the latest buzzwords in the cyber security industry is a ‘Zero Trust’ security model. In short, a zero-trust model basically means you do not leave any room for errors at all and do not trust anyone or anything.
Owing to a hybrid workplace led by the after-effects of the pandemic and several emerging technologies such as the Metaverse, Web 3.0, Augmented Reality and Virtual Reality, the cybersecurity industry is working hard as usual to be as future-ready as possible. But since we are yet to see the evolution of these technologies and its impact, we need to tread carefully when using these technologies.
So, what exactly is Zero trust? Is it a new product? Is it a certification or a mere buzzword within the cybersecurity industry?
Some organizations are mistaking zero-trust for an actual product or certification. A zero-trust model is not an actual product or new certification in the cyber security industry. A zero trust security model is deployed to ensure end to end cyber and cloud security. It is deployed for the security of our internal as well as external stakeholders. One of the most important concepts it lives by is ‘never trust, always verify’. It also includes enabling of multi-factor authentication in order to grant access to any application or platform. Additionally, it is also about embracing micro-segmentation of security perimeters to avoid any security breach.
Any new security features or model is not completely risk-free without building compliance and good habits among the employees. Similarly, zero trust is all about building good habits within your employees. It is also about ensuring that your employees enable multi-factor authentication when accessing any apps or platforms. It is an added form of compliance layer which shouldn’t be bypassed by the IT Admin, someone at the top level or even the deployer. There should be a top to bottom approach and a must for all employees to authenticated and validated continuously to build a better security posture within the organization.
A zero-trust model isn’t just about multi-factor authentication. It also requires all the users to be authenticated, authorized and have their security configurations continuously validated to access any kind of application or data. This is done as an additional layer of security. This model does have various benefits such as remote authentication and verification by your employees. This will allow them to work peacefully in a remote or a hybrid situation.
So, can you adopt the zero-trust model whenever you want?
Before deploying any new security model, we need to understand the return on investment. We need to know whether we really need it. We need to understand that while zero trust is an approach to secure the most important assets of the business, it’s equally as important to know whether the ‘juice is worth the squeeze’.
You already need to be a digital organization as you decide to deploy zero-trust security. For you to apply the zero-trust model within your organization, you need to be an already digital organization that has digital assets that need cloud and cyber protection. Your employees should have digital assets on which they can verify themselves.
We don’t need to jump into every bandwagon, deploy every new technology that is just launched. We need to understand our security needs first and then act accordingly. Your cyber security investments will only be worthwhile if you and your employees are willing to commit to it on a long-term basis and build good habits in order to ensure complete cyber security.
To read more news and exclusive features see our latest issue here.
Never miss a story… Follow us on:
 Security Buyer
 @SecurityBuyer
 @SecbuyerME
Media Contact
Rebecca Morpeth Spayne,
Editor, Security Portfolio
Tel: +44 (0) 1622 823 922
Email: [email protected]












