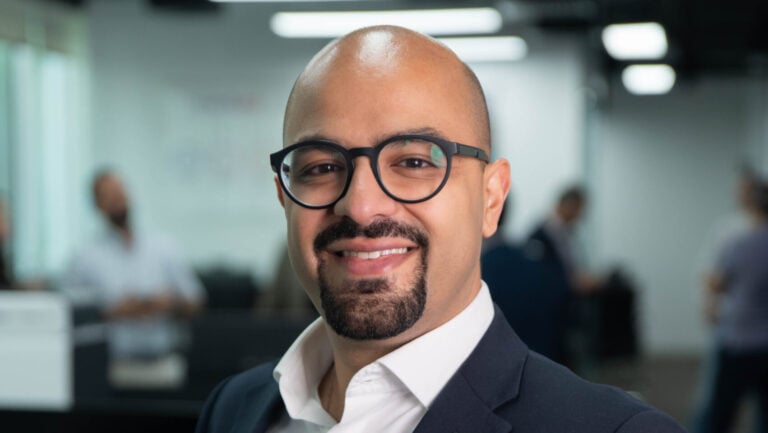
Michael Aminzade, VP of Consulting Advisory Services at Viking Cloud, discusses the state of cybersecurity in 2022
Cybercrime has been on the rise, with the first half of 2021 seeing a 93% increase from the same time in 2020. As a result, the state of cybersecurity has had to shift dramatically. This has made it a difficult subject to follow for many organisations. As businesses focus on the changing approaches to work and new expectations from customers, risks created by cybercrime are being treated as a low priority.
Part of the problem is a lack of basic understanding around the state of cybersecurity at large. This isn’t because of negligence, rather the landscape is shifting so much that it’s hard to keep track of. So, in this article, I will highlight three of the most significant changes to the state of cybersecurity in 2022. This way, it will be easier for an organisation’s cybersecurity team to know where to focus first on the ongoing battle against cybercrime.
Working From Home The last two years have been tarnished by the COVID-19 pandemic. To survive these turbulent times, organisations had to adapt – and not just to changes in cyberattacks. The pivot to working from home for many businesses came with concerns, but the proof has been in the pudding for many businesses who have prevailed in spite of COVID, highlighting it is possible for employees to work from home and still deliver. Whether a company allows working from home to continue long term will influence the digital security of the network.
The obvious issue with working from home is it introduces several more entryways into a network. Even if employees have company mandated laptops and phones updated to have the best digital security programmes covering them, the home network an employee would use would naturally have their own devices connected. Smart TVs, personal smart devices and even home computers won’t be protected by a business’s vulnerability management solution, making it a potential route for hackers to get onto a network.
While this might mean the better option would be to force employees to work back at the office to reduce security risks, this can have different consequences and produces other forms of security risk. An employee might prefer working from home, and being forced to come back into the office could lead to several social engineering issues. A lack of motivation to work leads to a lack of tact and care, which hackers can exploit. In the most extreme cases, it may even lead to an employee becoming an insider threat.
There are still a lot of challenges in this space that need tackling, and we will see that throughout 2022. Training employees about the risks working from home brings to both the business and their own personal data is a good start. Another tactic is to limit the number of third parties that come into contact with your data who lack any contractual obligation to keep it safe. There are multiple ways to achieve this; encryption, controlled access, virtual desktops data are just a few examples.
A less immediate action that can be taken by an organisation (but one that will surely help) is a shift in focus to how data is handled. Rather than focusing on what is trying to enter the network (especially with networks you don’t control and manage directly), a company should focus on limiting what can leave these networks. This can be done by introducing different network tiers and
controls with a mapping of what data can move between tiers. This will form the beginning of a third-party trust model. Limiting employee access to key data within the business from a “need to know” access model will also be a key part of the trust model. The shift won’t be an easy one, but in my opinion, it is a concept that needs to be adopted as part of a larger security program.
To read more exclusive features and latest news please see our Q4 issue here.
Media contact
Rebecca Morpeth Spayne,
Editor, Security Portfolio
Tel: +44 (0) 1622 823 922
Email: [email protected]