

Trellix, the cybersecurity company delivering the future of extended detection and response (XDR), today announced the establishment of the Trellix Advanced Research Center to advance global threat intelligence. Comprised of hundreds of the world’s most elite security analysts and researchers, the Advanced Research Center produces actionable real-time intelligence and threat indicators to help customers detect, respond and remediate the latest cybersecurity threats.
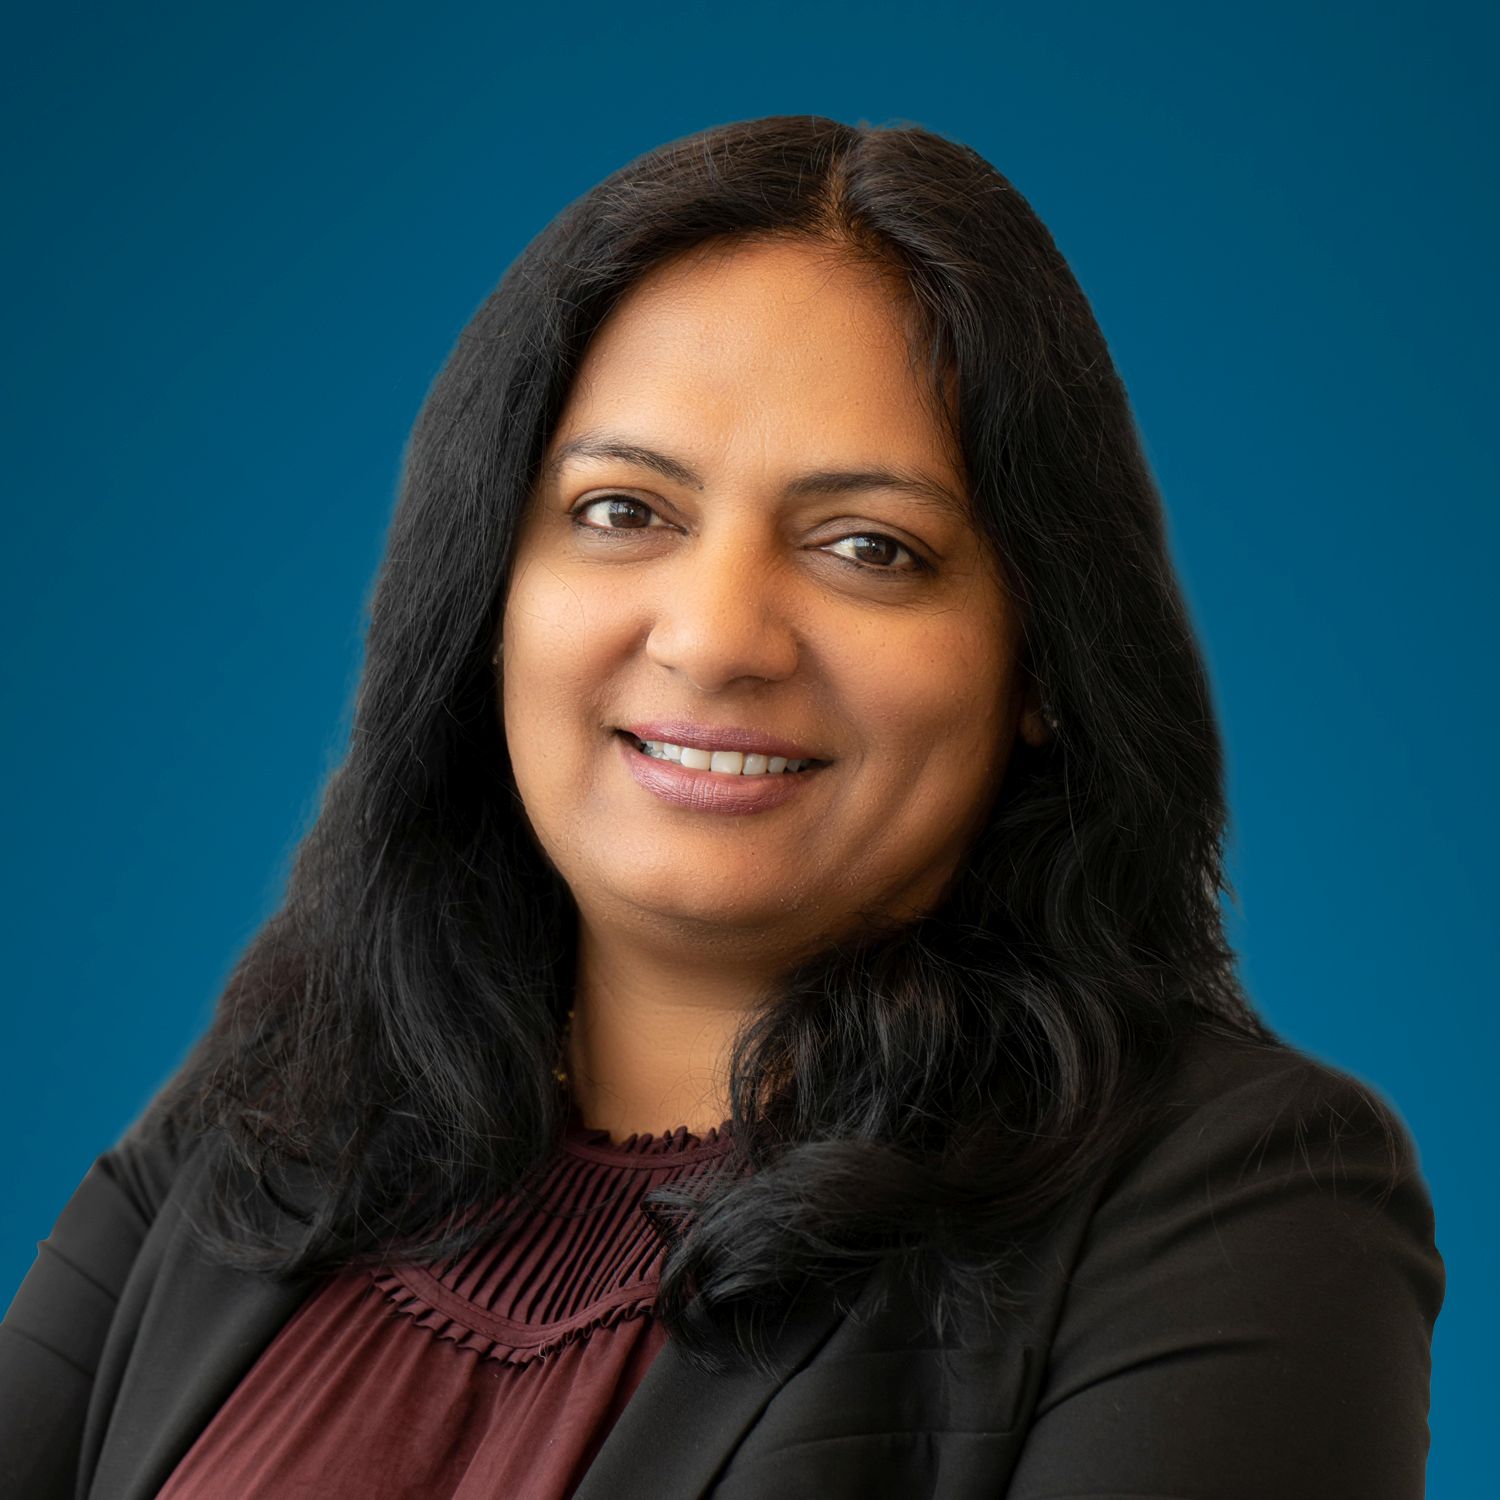
“The threat landscape is scaling in sophistication and potential for impact,” said Aparna Rayasam, Chief Product Officer, Trellix. “We do this work to make our digital and physical worlds safer for everyone. With adversaries strategically investing in talent and technical know-how, the industry has a duty to study the most combative actors and their methods to innovate at a faster rate.”
Trellix Advanced Research Center has the cybersecurity industry’s most comprehensive charter and is at the forefront of emerging methods, trends and actors across the threat landscape. The premier partner of security operations teams across the globe, Trellix Advanced Research Center provides intelligence and cutting-edge content to security analysts while powering our leading XDR platform.
Additional information can be found on the Trellix Advanced Research Center blog and in our Threat Center.
Python Tarfile Vulnerability Highlights Software Supply Chain Complexities
In coordination with today’s launch, Trellix Advanced Research Center also published its research into CVE-2007-4559, a vulnerability estimated to be present in over 350,000 open-source projects and prevalent in closed-source projects. It exists in the Python tarfile module which is a default module in any project using Python and is found extensively in frameworks created by Netflix, AWS, Intel, Facebook, Google, and applications used for machine learning, automation and docker containerization. The vulnerability can be exploited by uploading a malicious file generated with two or three lines of simple code and allows attackers arbitrary code execution, or control of a target device.
“When we talk about supply chain threats, we typically refer to cyber-attacks like the SolarWinds incident, however building on top of weak code-foundations can have an equally severe impact,” said Christiaan Beek, Head of Adversarial & Vulnerability Research, Trellix. “This vulnerability’s pervasiveness is furthered by industry tutorials and online materials propagating its incorrect usage. It’s critical for developers to be educated on all layers of the technology stack to properly prevent the reintroduction of past attack surfaces.”
Open-source developer tools, like Python, are necessary to advance computing and innovation, and protection from known vulnerabilities requires industry collaboration. Trellix is working to push code via GitHub pull request to protect open-source projects from the vulnerability. A free tool for developers to check if their applications are vulnerable is available on Trellix Advanced Research Center’s GitHub.
To read more news and exclusive features see our latest issue here.
Never miss a story… Follow us on:
 Security Buyer
 @SecurityBuyer
 @SecbuyerME
Media Contact
Rebecca Morpeth Spayne,
Editor, Security Portfolio
Tel: +44 (0) 1622 823 922
Email: [email protected]












